Methodology Note
This article examines China’s 9 October 2026 policy guidance through official government publications, accompanying regulatory interpretations, and relevant international machinery-safety and robotics standards references.
The analysis distinguishes verified policy statements from technical interpretation and proposed enterprise assurance practices. It uses an article-specific five-function decomposition—observation, detection, decision and enforcement, physical effect, and recovery—to examine how monitoring and warning claims differ from demonstrated physical containment. This decomposition is an analytical aid, not a formally established or independently validated ODA3 Institute framework.
Evidence sufficiency is considered using ODA3 Institute’s seven-stage assurance evidence chain: Requirement → Control → Evidence → Provenance → Verification → Finding → Bounded Assurance.
Chinese-language passages are presented as working translations rather than certified legal translations. No physical AI product, safety system, or operational deployment was independently tested. The warehouse example is illustrative, not an empirical case study.
The finding in brief
On 9 October 2026, the Communist Party of China Central Committee and the State Council issued the Opinions on Developing New Quality Productive Forces, a 19-measure industrial strategy document. Two passages matter for anyone buying, building or operating AI that moves in the physical world. The guidance names intelligent connected new-energy vehicles, humanoid robots, robotics and embodied intelligence among industrial and future-industry priorities. And in the same measure that orders the full implementation of the “AI Plus” initiative, it calls for building systems of technology monitoring, risk early warning and emergency response so that AI remains “safe, reliable and controllable.”
That pairing is the policy signal: support for physical-AI development alongside an expectation that monitoring, warning and response capabilities be built. It is not a robotics certification regime, a product standard or a directly enforceable duty on any company, and nothing published by the evidence cutoff turns it into one.
The analytical point this article develops is narrower and, for enterprises, more useful. Read in context, the guidance most naturally names monitoring, warning and response as national AI governance infrastructure. Either way, a buyer or operator cannot import that language as a control. For a robot, an autonomous vehicle or a drone, the decisive question is not whether hazards are monitored or warnings raised, but whether a specific machine can be shown to reach a safe physical state, in time, through a path that cannot be bypassed — and whether anyone can prove it afterwards. A warning is a claim about information. Containment is a claim about physics. Many of the artifacts that change hands in procurement — benchmarks, demonstrations, design descriptions — speak to the first rather than the second. That is an analytical caution about what such artifacts can establish, not a measured claim about how vendors behave.
The first question Boards should ask is interpretative, not technical: does this guidance impose an obligation on us, or does it describe a national capability? The text says the monitoring, warning and response systems are to be “built” to ensure AI safety, without naming who builds or operates them. Read in the context of a central strategy document addressing regions and departments, the more natural reading is a state and sectoral governance capability — oversight infrastructure — rather than an instruction to individual firms. A competing reading is that implementing measures will push equivalent duties down to developers and operators. Both are plausible; neither is established. Assessment: enterprises should not claim, and should not be told, that this passage imposes a present duty. They should monitor whether future implementing measures create developer or operator obligations; any resulting evidence requirements remain unestablished.
The same evidence question is arriving through other routes: the EU Machinery Regulation (EU) 2023/1230, which generally applies from 20 January 2027 and establishes machinery product-safety requirements and conformity-assessment routes, and the 2025 editions of ISO 10218-1 and ISO 10218-2 for industrial robot safety. Their scopes differ from those of driverless industrial trucks and other autonomous products. The legal applicability date, risk categories and specific standard clauses must be checked for each product rather than assumed. China’s guidance does not create these other routes, and they are not legally equivalent to it, but it adds a significant policy signal to the same question. For scale context, the International Federation of Robotics reported that China accounted for 54% of worldwide industrial-robot installations in 2024; this statistic does not measure humanoid or service-robot adoption [S12].
A second, restraining signal matters: Part VII of the guidance explicitly warns against speculative bubbles, blind investment and herd-like implementation, and calls for accountability when major losses result. The NDRC interpretation likewise stresses correcting blind investment and unfounded project expansion [S1][S2]. This tempers any claim that the policy simply mandates rapid scale-up.
For leadership, the decision that follows is concrete: before any autonomous system moves from controlled trial into space shared with people, vehicles or critical equipment, require evidence that its safe-state behaviour has been demonstrated at the physical level, across identified safety-relevant command paths, including remote and maintenance access, within a stated operating envelope — and treat what cannot be demonstrated as a reason to constrain the deployment, not as a residual line in a risk register.
What the guidance actually says
The full text was published on 9 October 2026. Its 19 measures sit under five headings: scientific and technological innovation, integration of technology and industrial innovation, new development approaches, institutional and mechanism innovation, and talent. Four measures bear directly on physical AI.
| Measure | What the Chinese text says (working translation, condensed) | What it is | What it is not |
|---|---|---|---|
| (7) Cultivating emerging industries | Accelerate strategic emerging industries including intelligent connected new-energy vehicles and robotics; develop the low-altitude economy and commercial spaceflight “on the premise of ensuring safety.” | Industrial priority-setting | A safety requirement for any product |
| (8) Future industries | Explore technology routes, application scenarios, business models and market-regulation rules for future industries including embodied intelligence. | Signal that regulatory rules for embodied AI are still being explored | Existing rules |
| (10) Full implementation of “AI Plus” | Accelerate scenario application of new-generation intelligent terminals including intelligent connected new-energy vehicles, AI phones and computers, and humanoid robots; build national AI industry-application pilot bases; build systems of technology monitoring, risk early warning and emergency response to ensure AI is safe, reliable and controllable. | The core passage: deployment plus a named safety architecture | A specification of what those systems contain, who operates them, or what an enterprise must do |
| (15) Market regulation | Strengthen governance in fields including AI; strengthen cross-department joint supervision; explore data-driven supervision. | Direction for regulators | A new enforcement mechanism |
Three further details shape interpretation.
First, the official English summary is a condensed version of the Chinese text. It reports the AI Plus initiative and the monitoring, warning and response systems, but it does not enumerate humanoid robots, intelligent connected vehicles or embodied intelligence. Readers relying on English coverage alone will understate how explicitly the guidance targets physical AI. This is editorial compression, not disavowal.
Second, the National Development and Reform Commission (NDRC) interpretation, published the same day by its High-Technology Department, describes AI as moving from the laboratory into production and daily life, giving rise to new fields including driverless vehicles, humanoid robots, autonomously flying drones and brain-computer interfaces. Under “safety assurance” it lists accelerating laws and regulations, policy systems, application norms and ethical guidelines alongside the monitoring, warning and response systems.
Third, and most relevant for anyone anticipating future rules, the NDRC explains the market-regulation measure as risk-differentiated and pilot-first: supervision content, method and frequency should vary by field and risk level; new supervisory rules should be piloted before being extended; uncertain areas may receive an “observation period”; and activities with large potential risk should face strict supervision. If new supervisory rules are developed through pilots — including the national AI industry-application pilot bases named in measure (10) — the evidence generated in those pilots is likely to shape what regulators eventually ask for. That is an inference, not a stated policy outcome; but operators and suppliers who can already produce structured, physical-level safety evidence would be better placed however implementation develops.
Context: the September standards-body framework
The guidance did not arrive in isolation. On 14 September 2026, China’s National Cybersecurity Standardization Technical Committee (commonly known as TC260), working under the guidance of the Cyberspace Administration of China, released AI Safety Governance Framework 3.0 at the opening of National Cybersecurity Week. The Cyberspace Administration’s announcement confirms the release and states that the framework continues the “risk classification, technical response, comprehensive governance” logic of versions 1.0 and 2.0 while updating its risk categories and measures. The announcement does not itself describe agent or embodied-AI provisions; secondary reporting describes version 3.0 as extending coverage to AI agents and embodied intelligence, with an annex dedicated to agent risk management.
ODA3 Institute did not analyse the full Framework 3.0 text for this article. Its agent and embodied-AI content is therefore treated as reported rather than verified, and nothing here depends on it.
Different jurisdictions, distinct obligations, related evidence questions
China’s guidance names an outcome — AI that is controllable — without saying how controllability is demonstrated. Separate machinery regulation and robotics standards have product-specific approaches to safety requirements and verification. This is an analytical comparison of evidence questions, not regulatory equivalence or harmonised enforcement.
The EU Machinery Regulation (EU) 2023/1230 generally applies from 20 January 2027 [S15], subject to its transitional and product-specific provisions, for machinery placed on the market. Its requirements for machinery and related products include product-specific safety and conformity-assessment routes. Regulation (EU) 2026/1744 of 8 July 2026, the “Digital Omnibus on AI”, amends the AI Act (EU) 2024/1689, Regulation (EU) 2018/1139 and the Machinery Regulation (EU) 2023/1230. Its title and amendment relationship are confirmed by the official EUR-Lex record [S6]; its operative changes to machinery obligations were not examined, and this article draws no conclusion about them. This is a separate legal regime, not an implementation measure of China’s guidance. Enterprises should determine their machinery category, transition period and conformity pathway rather than treating every ML-enabled device as subject to an identical procedure.
The 2025 editions of ISO 10218-1 and ISO 10218-2, the international safety standards for industrial robots and robot applications, specify requirements for inherently safe design, risk reduction and information for use. ISO 10218-1 explicitly excludes service robots, consumer products, medical robots, and mobility when robots are fixed to driverless industrial trucks or mobile platforms. For driverless industrial trucks, a category that includes certain autonomous mobile robots, ISO 3691-4:2023 specifies safety requirements and their verification; its published scope excludes remotely controlled trucks as a product category. This does not, by itself, exclude a driverless truck merely because it has a remote-support or maintenance interface; the functions and operating modes covered by the conformity assessment must be examined.
Scope matters in both directions. None of these instruments covers every humanoid, drone, road vehicle or medical robot, and an ISO standard binds only through a legal, regulatory or contractual basis. Equally, the October guidance does not start robotics safety from zero: existing machinery, occupational-safety, product-liability, functional-safety and cybersecurity rules may already govern a given product or facility, in China and elsewhere.
The cross-cutting engineering question is how product-specific safety, software-dependent protective functions and externally reachable command pathways are validated. The statutory duties and conformity pathways remain distinct. But a Board that approves a physical AI deployment on the strength of an AI benchmark and a vendor’s safety-function description is accepting less system-level evidence than machinery safety regimes and robot-safety standards, each in their own terms, already expect.
Monitoring is not control: five operational links
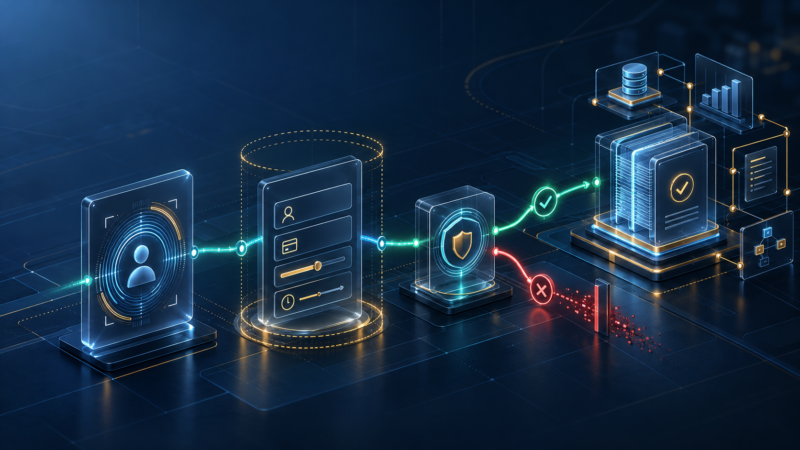
The phrase “monitoring, early warning and emergency response” describes a chain. In a physical AI system, every link has to hold, and each produces a different kind of evidence. Treating them as one capability can allow an assurance claim to outrun its evidence.
| Link | Question it answers | Evidence that supports it | Common overclaim |
|---|---|---|---|
| 1. Observe | Is the relevant physical and system state captured, attributable and current? | Timestamped, clock-synchronised records of pose, speed, mode, command source, sensor health, human proximity, bound to machine, firmware and model version | “We log everything” — without proof the logs are complete, current and attributable |
| 2. Detect | Is a hazardous condition recognised against a defined constraint? | Detection rules tied to the hazard analysis; tested true-positive and false-negative behaviour, including stale or missing data | An alert is treated as proof the hazard existed — or its absence as proof none did |
| 3. Decide and enforce | Does an authority with higher priority than the AI planner choose and impose the protective action? | Authority matrix; traces showing the safety controller rejecting or overriding unsafe commands; negative tests on every command route | A schematic shows separation that route-level testing has never confirmed |
| 4. Physical effect | Did the machine actually reach a safe state within the required time? | Independent physical measurement of motion and stopping, correlated with controller decisions | A STOP entry in the log is treated as a stopped machine |
| 5. Recover | Can operation resume only under authorised, verified conditions — and can the event be reconstructed? | Restart interlocks, operator takeover records, retained and tamper-evident evidence, retest after changes | Recovery is assumed because the system came back online |
These five operational links are an ODA3 analytical model, not a mandated reading of the national policy. They complement, and do not replace, ODA3’s assurance chain: Requirement → Control → Evidence → Provenance → Verification → Finding → Bounded Assurance. The two answer different questions. The five links describe what the system must do for a hazard to be contained. The seven-stage chain describes how an assurance conclusion about that system is built. Each link supplies a control and its evidence to the chain. A protective stop, for example, is the control; the controller trace and independent motion measurement are its evidence; tying both to the right machine, version and clock is provenance; repeating the test under adverse conditions is verification; and the result is a finding bounded to the tested envelope.
Links 1 and 2 are where the policy language — monitoring and early warning — naturally lands. Links 3 and 4 are where physical harm is prevented or not. A dashboard that raises a correct warning while the robot continues moving has satisfied the first half of the chain and failed the half that matters.
Two distinctions sharpen this.
Design independence is not evidence independence. A separate monitoring system may consume the same sensor feed as the planner it monitors; a redundant controller may share power, software or an administrative trust boundary. An independently recorded motion measurement strengthens a physical-effect claim, but even it does not by itself prove the stop was caused by the intended safety function rather than, say, a coincident fault. Causal correspondence requires deliberate test design: inducing the triggering condition, controlling alternative explanations, and repeating.
A control’s existence is several claims, not one. For any safety function, an organisation may know that the requirement is documented; that a control is designed; that it is implemented; that it was invoked during a test; that it produced the intended physical outcome; that the outcome was independently verified; and that the evidence supports a conclusion bounded to a defined envelope. A vendor document that establishes only design or invocation should not be read as proof of physical effect. Board approval for shared-space operation should rest on the last three.
Failure conditions worth designing tests around
These are generic engineering scenarios, not findings against any manufacturer, regulator or product:
- Sensor disagreement — perception reports a clear path while an independent proximity sensor indicates an obstruction.
- Stale command — a syntactically valid motion command arrives after the authorised operating mode has changed.
- Bypass through service access — a maintenance or remote-support interface reaches actuators without passing the intended supervisory gate.
- Alert without intervention — the warning fires but no protective action begins before the hazard develops.
- False safe-state record — logs report a stop while residual motion or stored energy persists.
- Untraceable fleet change — an update alters motion planning but the safety tests cannot be tied to the deployed version.
What different supplier artifacts can and cannot establish
Procurement is one place where this evidence distinction matters. The table compares illustrative supplier artifacts with what they do and do not establish. It reflects ODA3 Institute’s analytical judgement, not a survey of vendor practice.
| Typically offered | What it can establish | What it does not establish | What to request |
|---|---|---|---|
| AI model benchmark | Model performance on a defined dataset | Behaviour of the integrated machine; safety under faults | System-level hazard analysis and safe-state test results |
| Simulation or demonstration video | Behaviour in the depicted conditions | Coverage of degraded, adversarial or out-of-envelope conditions; reproducibility | Test protocol, conditions, failure cases and exclusions |
| Safety-function description | Design intent | Implementation, invocation or physical effect | Controller-disposition traces with independent motion measurement |
| Standards conformity claim | Conformity to that standard’s stated scope | Coverage of modes or interfaces outside that scope (for example, remote operation, which ISO 3691-4:2023 explicitly excludes ) | The scope statement and how out-of-scope paths are controlled |
| Penetration test report | Exposure of tested interfaces at a point in time | Safety behaviour; coverage of untested routes; post-change validity | Route inventory and bypass tests on actuator-reaching paths |
| Incident or uptime statistics | Reported operating history | Independence or completeness of that reporting | Incident definitions, data provenance and evidence-access rights |
What leadership should decide
The guidance gives Boards no new legal duty, but it gives them a useful prompt. The governing question is: what must be demonstrated before an autonomous system moves from controlled trial into production space shared with people, vehicles or critical infrastructure — and who decides when that evidence is incomplete?
| Decision | Accountable owner | Evidence that would justify it | Escalation trigger |
|---|---|---|---|
| Authorise a production pilot | COO with Safety Director | Hazard analysis; physical safe-state tests in the defined envelope; named residual-risk owner | Containment of hazardous motion not demonstrated at the physical level |
| Permit vendor remote access or remote support | CISO with Engineering | Identity and session controls; route-level bypass tests; access logs available to the operator | Any actuator-reaching path untested or not disclosed |
| Expand speed, payload, site or hours | COO with risk owner | Change-impact assessment and physical retest | Operation beyond the validated envelope |
| Approve a supplier for fleet roll-out | Procurement with Chief Risk Officer and General Counsel | Safety case; negative-test results; contractual evidence, incident-cooperation and change-notification rights | Supplier declines access to safety-critical evidence |
| Accept an unresolved unknown | Risk Committee | Explicit statement of what is unknown, why, and the compensating constraint | No owner, no constraint, or no date for resolution |
For the CEO and COO, the risk profile changes at the transition from pilot to fleet. Approve envelope expansion in stages, each gated on evidence, rather than approving autonomy as a single decision.
For the CFO, the guidance provides no basis for estimating returns or loss probabilities, and this article offers none. What can be specified is the structure of the cost that is routinely omitted. A defensible business case treats total assurance cost over the deployment period as approximately: initial validation + (number of material changes × retest cost per change) + evidence infrastructure and retention + operator training + incident investigation capacity + expected downtime from constrained operation. Each term is organisation-specific; the useful discipline is requiring that every term is estimated, with its range and assumptions stated, before capital approval. Change-driven retesting deserves explicit analysis because software, payload and environment changes can invalidate previously tested conditions; its actual cost depends on the deployment.
For the CISO and Safety Director, ownership is shared but not interchangeable. Cybersecurity protects identities, networks, software and command integrity; functional safety addresses hazardous physical outcomes and required protective behaviour. A penetration test is not a machinery safety validation; a safety certificate may not cover a remote interface added after certification. The command boundary — every path by which anything can make an actuator move — should be jointly approved.
For General Counsel and Procurement, determine which requirements actually bind a given product in a given market before anyone claims conformity, and do not represent a Chinese strategy document as a global compliance obligation. Contractually, the most valuable protections are evidence rights: access to safety-critical logs, notification of software changes affecting motion or safety, and cooperation in incident investigation.
Questions directors can ask management: What physical condition would force us to stop this deployment, and how fast? How do we know a stop command stopped the machine? Which vendor actions can reach actuators without passing our controls? Which changes invalidate our last test? Where evidence is missing, who owns that decision?
Implementation: a staged evidence sequence
The following sequence is a proposed practitioner workflow derived from the five-link model. It is not drawn from China’s guidance, and it is not a legal certification procedure. It complements, and does not replace, hazard analysis, prescribed test methods, accredited safety assessment or any certification the product requires. A cybersecurity route test can establish access-control behaviour but not functional safety; a safety certificate does not necessarily establish the security of remote-access paths added after deployment.
Stage 0 — Obligations and authority. Identify the jurisdiction, site, sector, equipment class and function; separate policy direction from enforceable machinery, occupational-safety, cybersecurity, data-protection and product obligations; name who may approve installation, change operating modes and accept residual risk. An AI-framework mapping is not a substitute for this legal analysis. Artifacts: obligation register; safety ownership; approval and exception records.
Stage 1 — System and physical envelope. Inventory sensors, compute, controllers, actuators, firmware, remote interfaces, network dependencies and mechanical constraints. Define the validated payload, speed, surface, lighting, human proximity and operating modes, and state what is out of scope. Artifacts: configuration baseline; hazard analysis; boundary diagram; operating envelope.
Stage 2 — Command authority and no-bypass. Trace every path from AI planning to actuator effect, including maintenance, recovery, remote-support and emergency routes. Test that safety functions take priority and cannot be overridden by the planner or an unauthorised credential. Artifacts: authority matrix; command-route inventory; positive and negative traces; bypass-test results.
Stage 3 — Detection-to-effect timing. Take hazard thresholds and required reaction times from the safety analysis; a qualified safety professional should define safe-state criteria and which fault injections are permissible before any test runs. In a controlled environment, inject sensor faults, communications loss, stale state and conflicting commands, and measure the interval from detection to decision to commanded intervention to physical effect. Synchronise clocks, and use independent physical measurement where software timestamps cannot establish the effect. Artifacts: test protocol; synchronised logs; independent motion measurements.
Stage 4 — Recovery, change and incident readiness. Test safe restart, rollback and operator takeover; define which software, sensor, payload or environmental changes trigger retesting; confirm evidence is retained and preserved in a way that supports reconstruction. Artifacts: recovery protocol; change-impact criteria; retest history; evidence-preservation plan.
Stage 5 — Bounded findings and decision. For each safety claim, record what the evidence supports, with the test identifier and source artifact; list what was not tested and what was refused. Where a critical property remains unknown, constrain, defer or retire the use case. Artifacts: bounded finding register; Notably Absent list; accountable risk acceptance; procurement decision.
In an actual hazard, human safety procedures and emergency responders take priority over forensic completeness. Once the scene is safe, preserve configuration, command and controller records, sensor histories, operator actions and independent observations, without asserting a root cause prematurely. A collision can arise from interacting mechanical, operational, software and human factors; the presence of AI in a system is not proof of AI causation.
Worked example: an autonomous mobile robot in a shared warehouse
Illustrative scenario. No manufacturer, warehouse or product was tested.
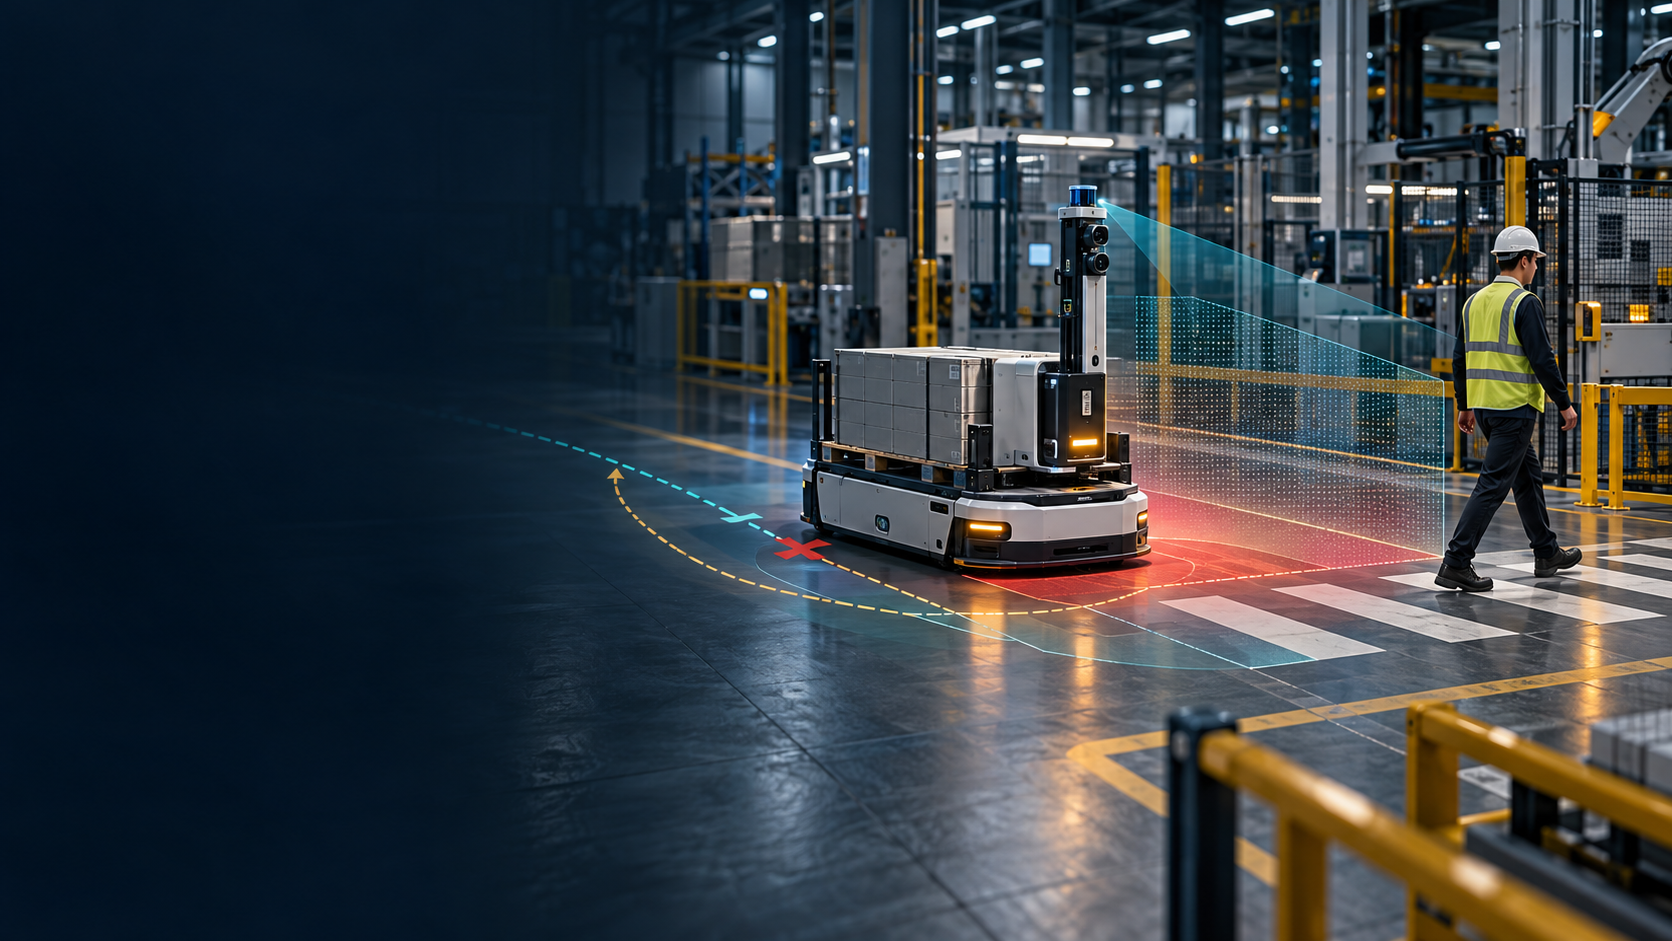
A logistics operator plans to deploy autonomous mobile robots moving pallets between loading bays and storage, during shifts when pedestrians and forklifts use adjacent routes. The supplier provides a perception benchmark, a simulation video, a safety-function description and a statement of conformity to the relevant driverless-truck safety standard.
The assurance team frames one bounded question: Does the robot reach a controlled stop before entering a pedestrian crossing when localisation confidence degrades, at maximum authorised payload and speed?
The team records machine identity, software and safety-controller versions, payload, route, floor condition and sensor state, then induces a controlled localisation fault. The AI planner continues to issue a motion command; the safety controller is expected to override it. The team captures the planner command, the controller’s disposition and an independent measurement of the robot’s motion and stopping distance, repeating the test several times. It then repeats the sequence with the supplier’s remote-support session active, to probe whether that route can reach the drive system without passing the safety controller.
Suppose the normal-path tests show consistent controlled stops, but the supplier declines to provide technical detail on the remote-support path, and the conformity statement does not specify whether the remote-support pathway and relevant operating modes were assessed. The ISO exclusion for remotely controlled trucks cannot resolve this question without examining the actual configuration and conformity scope. The defensible findings are:
- Normal-path safe-state behaviour: supported, within the tested envelope and conditions.
- No-bypass through remote support: unknown — not tested to a conclusion; coverage by the supplier’s conformity assessment has not been established.
- Behaviour outside the tested envelope (wet floors, mixed loads, sensor degradation combined with communications loss): not examined.
What this establishes is that one safety function works on one path under defined conditions. What it does not establish is that the deployment is safe. A reasonable decision is to approve operation with remote support disabled or gated by on-site authorisation, restrict the operating area, require supplier evidence on the remote path as a contractual condition, and defer unrestricted shared-space operation. The Board should hear exactly that — not that the system has been “assured.”
This is where policy language and operational evidence meet. A commitment to monitoring and emergency response becomes useful only when a specific protective action, and its physical effect, can be demonstrated.
Where ODA3 frameworks apply
ODA3 Institute’s frameworks offer structure for this work; they do not change what the evidence shows.
PAI-SF™ v1.0, the Physical AI Security Framework, is built for systems that sense, decide and act in the physical world, on the principle of Kinetic Zero Trust: physical commands are never trusted on model confidence or authorisation alone, but validated against independent safety boundaries. Its domains on actuator and kinetic command safety, safe-state and degraded-mode behaviour, human override, runtime monitoring and the functional-safety interface correspond closely to links 3 to 5 above. GAISSF™ v1.0 provides the surrounding governance context — accountable ownership, change control, third-party assurance and risk acceptance. UAIF™ v1.0 keeps incident records precise, so that a blocked command, a near miss and an injury remain distinct events with explicit attribution confidence. AI-IRF™ v1.0 structures response and recovery, including the recognition that physical containment may require local isolation rather than revoking a cloud credential.
The bounded-finding approach used in the worked example follows the practitioner method published in How to Assess an AI System (ODA3-2026-08-WHP-COM-020): one system, one question, explicit provenance, negative and inconclusive results kept distinct. Finding states such as “supported” and “unknown” are descriptive aids, not scores, severity grades or certification decisions.
None of this implies that China’s guidance references or endorses these frameworks, that ODA3 Institute has examined any Chinese deployment, or that applying a framework constitutes conformity assessment or certification.
Notably Absent
The following were looked for and not found in the sources reviewed, or were outside the boundary of this analysis:
- Implementing detail for measure (10): no specification of what the monitoring, warning and response systems contain, who operates them, or what is expected of developers, operators or buyers.
- Deadlines, conformity routes and enforcement: no implementation deadline, named conformity-assessment body, certification scheme or enforcement mechanism attached to the new passages.
- Machine-level test requirements: no safe-state, response-time or bypass-testing requirement for robots, vehicles or drones.
- Effectiveness evidence: no data on the performance of any existing monitoring, warning or response system for AI in China.
- Deployment and incident data: no independent fleet incident data, and no evidence that any named product has passed or failed safe-state testing. This article makes no claim that any supplier is deficient because a public test report was not located.
- Not reviewed: the full text of AI Safety Governance Framework 3.0 (release confirmed by the official announcement; content reported); existing Chinese national and sector standards for robots and vehicles, which may apply independently; the full ISO 10218 and ISO 3691-4 texts (published scope statements only); the operative text of the EU Machinery Regulation and of Regulation (EU) 2026/1744; and product-level EU classification.
Limitations
The guidance is a central policy document written in Chinese; the translations here are working translations, and the interpretive judgements — particularly that measure (10) describes a governance capability rather than an enterprise duty — are analytical assessments that implementing measures could overturn. Developments after 13 October 2026 are not reflected. The vendor-evidence table and the five-link model are ODA3 Institute’s analytical constructs, not empirical findings about industry practice.
Conclusion
China’s October guidance joins support for physical-AI development — tempered by explicit warnings against blind expansion — with an expectation that AI be monitored, warned about and responded to. Neither half tells an enterprise what to prove. The defensible response is neither to claim alignment with a policy that imposes no direct duty nor to treat a strategy document as a threat. It is to recognise the question that machinery regulators, standards bodies and Boards each ask in their own terms: not whether a hazard can be seen, but whether a specific machine can be shown to stop.
Start with one system and one hazardous action. Establish who and what can command it, which independent function can prevent or halt the action, how the physical effect is measured, what was not tested, and who accepts what remains unknown. Keep negative findings and the operating envelope visible to the people who approve the deployment. That is how a policy commitment to safety becomes evidence of it.
Sources
- [S1] China Government Network (gov.cn, State Council General Office; authorised Xinhua release), 中共中央 国务院关于发展新质生产力的意见 (Opinions of the CPC Central Committee and the State Council on Developing New Quality Productive Forces), full Chinese text, 9 October 2026. Measures (7), (8), (10), (15) and Part VII. https://www.gov.cn/yaowen/liebiao/202610/content_7082819.htm — same text also published by the National Data Administration: https://www.nda.gov.cn/sjj/swdt/xwfb/1009/20261009191908259329235_mobile.html
- [S2] National Development and Reform Commission, High-Technology Department, 国家发展改革委有关负责同志就《关于发展新质生产力的意见》答记者问 (official Q&A), 9 October 2026. https://www.ndrc.gov.cn/xwdt/xwfb/202610/t20261009_1408037.html
- [S3] State Council of China (English portal, Xinhua), China issues guidelines on developing new quality productive forces, 9 October 2026. https://english.www.gov.cn/policies/latestreleases/202610/09/content_WS6ac8d93ec6d00ca5f9a0d95c.html
- [S4] Cyberspace Administration of China, 《人工智能安全治理框架3.0》发布 (release of AI Safety Governance Framework 3.0 by the National Cybersecurity Standardization Technical Committee, 全国网络安全标准化技术委员会), 14 September 2026. https://www.cac.gov.cn/2026-09/14/c_1791137092283345.htm
- [S5] MLex, China updates AI safety framework to address agent, embodied-AI risks, 15 September 2026 (secondary reporting on Framework 3.0 content). https://www.mlex.com/mlex/articles/2524830
- [S6] EUR-Lex, Regulation (EU) 2026/1744 of 8 July 2026 amending Regulations (EU) 2024/1689, (EU) 2018/1139 and (EU) 2023/1230 (Digital Omnibus on AI) — official record; operative text not examined. https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX:32026R1744
- [S7] EUR-Lex, Regulation (EU) 2023/1230 on machinery — official record. https://eur-lex.europa.eu/eli/reg/2023/1230/oj/eng
- [S8] Baker McKenzie, Product Risk Radar: Machinery Regulation, updated November 2025 (application date and structure). https://www.bakermckenzie.com/en/insight/publications/resources/product-risk-radar-articles/machinery-regulation
- [S9] ISO, ISO 10218-1:2025 Robotics — Safety requirements — Part 1: Industrial robots, published scope. https://www.iso.org/standard/73933.html
- [S10] BSI Knowledge, BS EN ISO 10218-1:2025, scope exclusions including mobility on driverless industrial trucks and mobile platforms. https://knowledge.bsigroup.com/products/robotics-safety-requirements-industrial-robots-1
- [S11] ISO, ISO 3691-4:2023 Industrial trucks — Safety requirements and verification — Part 4: Driverless industrial trucks and their systems, published scope. https://www.iso.org/standard/83545.html
- [S12] International Federation of Robotics, World Robotics 2025 China press release, 25 September 2025. https://ifr.org/downloads/press_docs/2025-09-25-IFR_press_release_China_in_English.pdf
- [S13] ODA3 Institute, PAI-SF™ v1.0 Physical AI Security Framework library, accessed 13 October 2026. https://docs.oda3.org/frameworks/pai-sf/
- [S14] ODA3 Institute, How to Assess an AI System (ODA3-2026-08-WHP-COM-020), accessed 13 October 2026. https://docs.oda3.org/documents/com-020/
- [S15] European Agency for Safety and Health at Work (EU-OSHA), Regulation 2023/1230/EU — Machinery, official EU agency legislation summary, accessed 13 October 2026; confirms general application from 20 January 2027. https://osha.europa.eu/en/legislation/directive/regulation-20231230eu-machinery
Evidence and Analytical Status Ledger
Evidence Confidence uses ODA3’s standard tiers (T1 Primary Verified; T2 Secondary Verified; T3 Controlled Simulation / Academic Proxy; T4 Anecdotal / Unverified). Analytical Status classifies the kind of claim.
| # | Claim | Source | Evidence Confidence | Analytical Status |
|---|---|---|---|---|
| L1 | Guidance issued 9 Oct 2026 by CPC Central Committee and State Council; 19 measures in five areas | S1, S3 | T1 | Verified Fact |
| L2 | Measure (10) names intelligent connected new-energy vehicles and humanoid robots and calls for technology monitoring, risk early warning and emergency response systems | S1, S3 (partial) | T1 | Verified Fact |
| L3 | Measures (7) and (8) cover robotics, the low-altitude economy “on the premise of ensuring safety,” and exploration of market-regulation rules for embodied intelligence | S1 | T1 | Verified Fact |
| L4 | English summary does not enumerate humanoid robots, intelligent connected vehicles or embodied intelligence | S3 compared with S1 | T1 | Verified Fact |
| L5 | Part VII and the NDRC warn against bubbles, blind investment and herd-like duplicated projects, with accountability for major losses | S1, S2 | T1 | Verified Fact |
| L6 | NDRC lists driverless vehicles, humanoid robots, autonomous drones and brain-computer interfaces; lists laws, norms, ethical guidelines and the monitoring/warning/response systems under safety assurance | S2 | T1 | Verified Fact |
| L7 | NDRC describes supervision as risk-differentiated and pilot-first, with observation periods | S2 | T1 | Verified Fact |
| L8 | No implementing deadline, conformity route or machine-level test requirement attached to the new passages | S1, S2, S3 reviewed | T1 (absence within reviewed sources) | Corroborated Observation |
| L9 | Measure (10) more naturally describes a governance capability than a present enterprise duty | S1, S2 | — | Analytical Assessment |
| L10 | Pilot-generated evidence likely to shape future supervisory expectations | S1 (pilot bases), S2 (pilot-first) | — | Hypothesis |
| L11 | TC260 released Framework 3.0 on 14 Sep 2026 under CAC guidance, continuing the risk-classification / technical-response / comprehensive-governance logic | S4 | T1 | Verified Fact |
| L12 | Framework 3.0 extends coverage to agents and embodied intelligence | S5 and further secondary reporting | T2 | Corroborated Observation (full text not reviewed; not stated in S4) |
| L13 | EU Machinery Regulation generally applies from 20 Jan 2027 | S7, S15 (EU agency summary) | T1 (institutional summary; primary regulation article not extracted) | Verified Fact (general application date; product-specific routes not examined) |
| L14 | Regulation (EU) 2026/1744 amends the AI Act, Regulation 2018/1139 and the Machinery Regulation | S6 | T1 (official record title) | Verified Fact (relationship only; effect on machinery obligations Unknown) |
| L15 | ISO 10218-1:2025 covers industrial robots; excludes medical, service and consumer robots and mobility on driverless trucks or mobile platforms | S9, S10 | T1 / T2 | Verified Fact (published scope) |
| L16 | ISO 3691-4:2023 covers driverless industrial trucks including autonomous mobile robots; excludes remotely controlled trucks | S11 | T1 (published scope) | Verified Fact |
| L17 | China accounted for 54% of global industrial-robot installations in 2024 | S12 | T1 (data owner’s release; methodology not independently reproduced) | Verified Fact (as reported by IFR) |
| L18 | PAI-SF™ v1.0 is published as Final Publication, built on Kinetic Zero Trust | S13 | Publisher page, checked live 13 Oct 2026 | Verified Fact (publisher statement; not independent validation) |
| L19 | Five-link model, seven-stage chain mapping, supplier-artifact table, staged sequence and cost structure | ODA3 Institute analysis | — | Analytical Assessment |
| L20 | Warehouse worked example | Constructed | — | Hypothesis (illustrative) |
GAISSF™, UAIF™, AI-IRF™ and PAI-SF™ are frameworks of ODA3 Institute, referenced under the GAISSF Ecosystem Licence (GEL) v1.0.
© 2026 ODA3 Pvt Ltd
Methodology note
Desk-based policy and technical research using official Chinese government publications, regulatory interpretations, EU regulatory references, and published robotics standards information. Material claims are distinguished as verified facts, reported information, analytical assessments, hypotheses, or not established, according to the supporting evidence. Five operational functions (observation, detection, decision/enforcement, physical effect, recovery) are used as an article-specific analytical decomposition, not an established ODA3 framework. Assurance reasoning follows the ODA3 seven-stage evidence chain (Requirement → Control → Evidence → Provenance → Verification → Finding → Bounded Assurance). Chinese translations are working translations, not certified. No independent robot testing, deployment assessment, product conformity evaluation, proprietary telemetry analysis, or empirical case study was performed. Verification limitations and excluded conclusions are maintained in the article's evidence ledger and Notably Absent section.
Notably Absent
No machine-level implementation protocol, universal enterprise deadline, or conformity-assessment procedure established by the October guidance was identified in the reviewed sources. No specific robotics deployment, safety controller, physical-effect containment mechanism, or command-path bypass control was independently tested. No original operational telemetry, fault-injection results, or product-specific safety-validation evidence was examined. Full technical standards, controlling ODA3 methodology documents, and product-specific legal applicability were not comprehensively verified in this research pass. No independent product assurance, regulatory conformity, continuous effectiveness, or manufacturer-specific safety conclusion is claimed. Absence of evidence in this review is not evidence of absent controls or manufacturer non-compliance.