An authenticated customer session does not, by itself, establish the scope of an AI agent’s authority. Banks and insurers need a traceable link from permitted action to executed transaction.
Executive takeaways
- Separate identity authentication, standing mandates, specific approval and actual execution; each answers a different evidential question.
- Require enforceable limits and linked records for agent-initiated payments, including rejected changes, retries and exceptions—not only successful logins.
- Before making underwriting representations, distinguish controls described by management from controls independently examined in a defined operating period.
The decision is whether an AI agent’s payment authority can be demonstrated
A customer tells a banking assistant to pay suppliers within agreed limits. The AI agent identifies an invoice, selects a beneficiary and initiates payment. The customer previously authenticated and may have accepted a broad standing mandate. Whether that mandate covered the particular payment cannot be answered from the authentication event alone.
This article presents an evidence-design analysis, not findings from an examined bank deployment, insurance claim or customer dispute. For the bank, this is a transaction-control and potential customer-dispute issue. For its board, the immediate decision is whether the product may initiate or alter consequential transactions without a demonstrable authority boundary. For an insurer evaluating AI-related exposure, it is a question of what the institution can substantiate about its control environment. A record of who authenticated is not a complete record of what was authorised.
A fresh customer prompt for every action is not the only valid control. Valid standing instructions may cover defined repeat activity. What matters is whether permitted amounts, recipients, conditions, timing, delegation and modification rules were established, enforced and traceable to execution.
India’s public sources distinguish AI governance from payment controls
India offers two related but distinct reference points. The Reserve Bank of India (RBI) published its Committee report on the Framework for Responsible and Ethical Enablement of Artificial Intelligence (FREE-AI) on 13 August 2025. Its seven guiding principles include People First and Accountability. In section 4.3.1, the committee says human judgment and citizen interests should remain central, and that accountability for AI outcomes rests with deploying entities regardless of autonomy. The committee also recommends AI-aware product approval, consumer protection and governance measures. These are committee recommendations and principles, not, simply by publication, a newly enacted technical mandate requiring cryptographic binding of every AI payment approval. [1]
The RBI also issued the Authentication Mechanisms for Digital Payment Transactions Directions, 2025 on 25 September 2025, with a general compliance date of 1 April 2026, subject to exceptions stated in the instrument. In paragraph 5, RBI defines authentication as the process of validating and confirming the credentials of the customer originating a payment instruction. That definition addresses credential verification; it does not, by itself, determine whether an AI agent’s resolved amount, beneficiary or delegation remained inside the customer’s mandate. The latter is a separate operational and, where disputed, legal question. [2]
A separate bank-specific instrument is relevant but has not been examined clause by clause. RBI’s official Master Directions index lists the Commercial Banks – Digital Payment Security Controls Directions, 2026, issued 31 July 2026, with an edition updated as of 1 October 2026. Its scope makes it relevant to commercial banks’ existing digital-payment controls, rather than treating agentic payments as a wholly new control category. The operative consolidated clause text was not examined for this analysis. Accordingly, this article makes no claim about requirements for AI-initiated payments under that instrument, including particular beneficiary-change obligations, settlement deadlines or AI-specific mandates. Banks should assess their existing payment controls against the current official text before adding or representing new agent-specific controls. [3]
The FREE-AI committee report itself discusses agent-executed transactions and AI-specific manipulation risks, including prompt-injection-induced unauthorised transfers. That establishes that the risk mechanism is part of RBI committee analysis; it does not demonstrate an observed incident in a particular bank or a measured industry loss rate. [1]
The transferable analytical point is narrower than a claim of global legal uniformity: wherever a system acts under delegated instructions, a reviewer needs to identify the governing mandate and the facts that show whether a given action stayed within it. The legal effectiveness of the instruction and its authentication mechanism remains jurisdiction- and product-specific. The transferable method is to identify the governing mandate, check how an action was resolved, and test whether execution stayed inside the applicable boundary; no cross-jurisdiction legal equivalence is claimed.
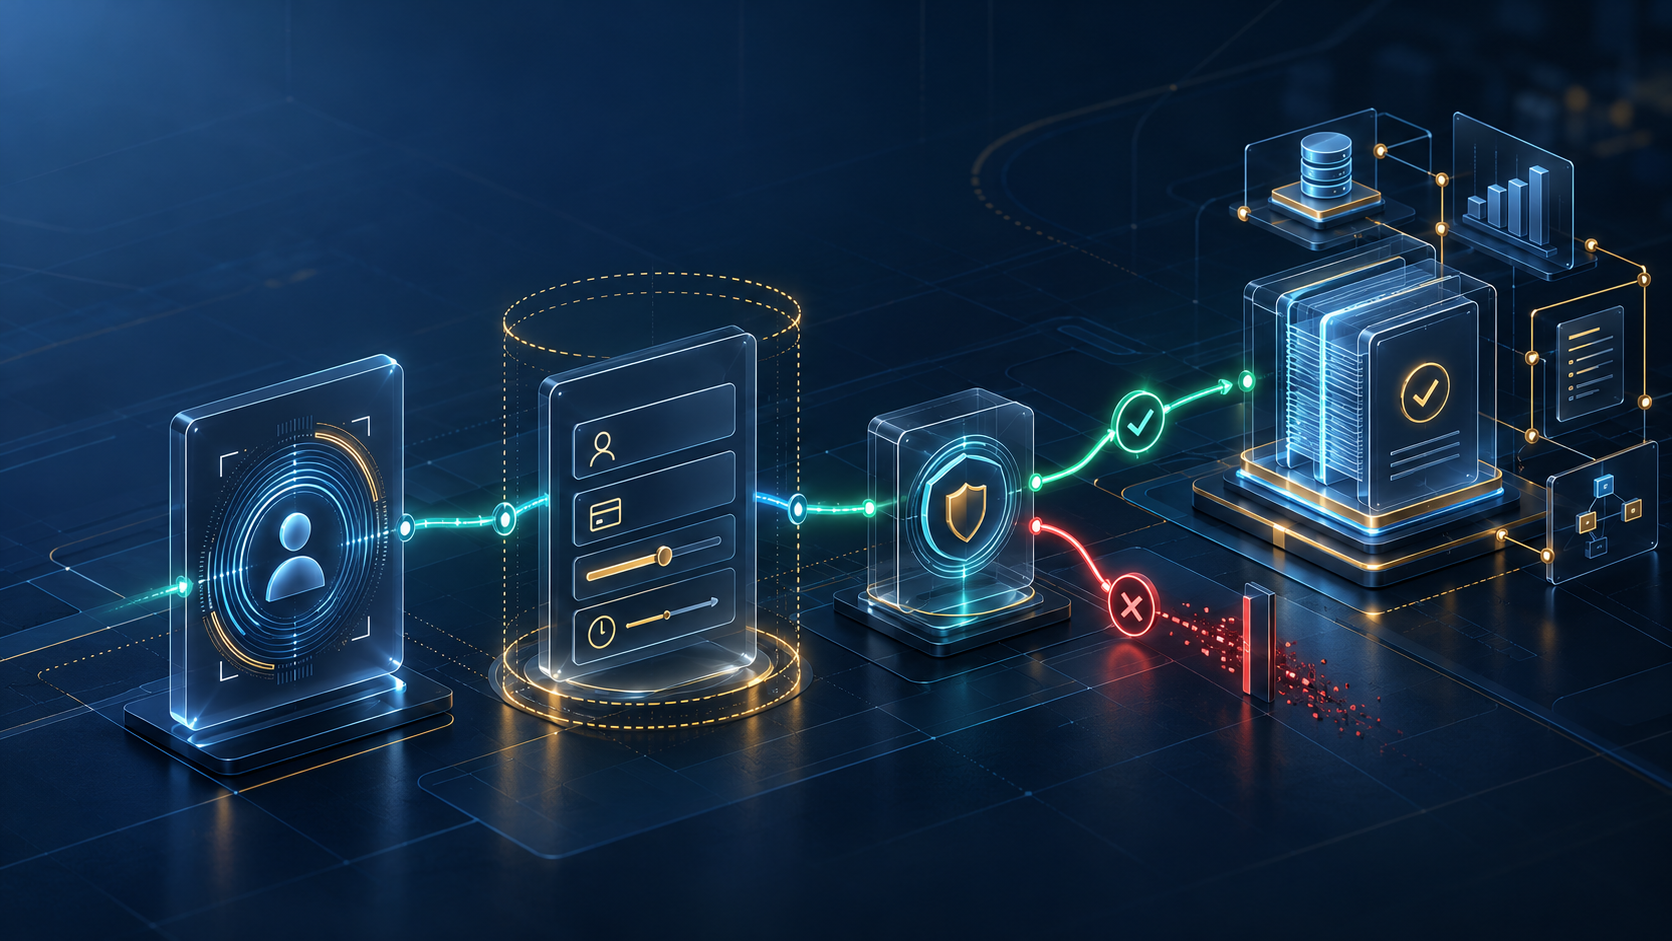
Four records answer four different questions
Identity authentication: Which customer, representative, device or credential was authenticated, and under what mechanism? This can support attribution of an event, but it need not establish the scope of downstream transactions.
Delegated authority: What permitted actions did the customer or corporate signatory authorise? The answer may be in an approved mandate, account authority, workflow rule or transaction-specific instruction. Relevant terms can include payment account, eligible payees, amount and frequency ceilings, purpose, expiry and allowed sub-delegation. In a mandate-based payment, the recorded terms may also include the trigger condition and which data source determines whether it has been met.
Approval and policy enforcement: When the agent resolved an instruction into actual payment details—or changed a beneficiary, amount or route—did the operative authority policy permit the change? Was further approval required? Did the system enforce a block when a change exceeded scope?
Executed transaction: What was actually sent to the payment rail, accepted or rejected, and ultimately reconciled? Records should permit a reviewer to compare resolved instructions and policy decisions with the final transaction rather than assuming that a successful API call proves approval.
For consequential transactions, ODA3 Institute’s analysis favours an enforceable decision point outside the agent’s natural-language reasoning, supported by correlated records whose completeness, integrity and accuracy can be tested. Cryptographic signing may be appropriate, but a cryptographic signature is not a universal legal prerequisite or a substitute for correct scope definition, complete event capture or valid consent.
A reported mandate-based payment model makes the question concrete
In a 11 June 2026 announcement, Pine Labs described its Pine Labs Payment Protocol (P3P) as enabling AI agents to complete certain Unified Payments Interface (UPI) payments against customer-approved mandates without fresh authentication at the moment of each payment. The company identified digital-gold platform Gullak as live with the model. Its published developer documentation describes both one-time mandates and UPI ReservePay as available payment methods. These are company-reported capabilities and deployment status, not independently verified payment outcomes or regulator approval. [4][5]
The relevance is the distinction between approval of the standing mandate and evidence that a particular later debit conformed to it. A rule such as a spending ceiling plus a market-price trigger requires more than a record of successful mandate creation: the reviewer may also need the trigger definition, the price source and time, the resolved payee and amount, the operative policy decision and the debit result. This article has not tested P3P, Gullak, their mandate interpretation, enforcement, regulatory compliance or operating effectiveness. The example does not imply any product defect.
A synthetic payment illustrates the evidence break
Illustrative scenario — synthetic, not based on an examined system.
A corporate customer instructs an AI-enabled accounts-payable assistant in its bank’s business-payments portal: Pay Supplier A’s current invoice from Account X before Friday, subject to a ₹250,000 ceiling. The assistant processes a later document containing replacement bank details. It proposes a payment of ₹248,000 to a different beneficiary.
The proposed amount is below the ceiling; the beneficiary no longer matches the instruction. Neither the earlier authenticated login nor the value threshold answers whether the new payee was authorised. The institution’s controls would need to reject the change, obtain a valid new approval or establish that an existing mandate expressly permitted the substitution.
For examination, the relevant chain is: original instruction and authority version → retrieved data and resolved beneficiary → change detection → policy decision → any approval → payment instruction → transaction result and reconciliation. A partial chain may leave the scope question Unknown (insufficient evidence); affirmative evidence of an unauthorised substitution under explicit criteria could show a Gap (demonstrated departure from a requirement). This scenario asserts no real payment, loss, complaint, legal ruling or insurance outcome. Existing bank controls for beneficiary changes are a baseline for examination; the additional question is whether the same controls apply when an agent resolves or substitutes the beneficiary.
The bank–insurer evidence exchange has two directions
This article concerns underwriting the risks arising from an organisation’s use of AI, not the different topic of an insurer using AI to make underwriting decisions.
Insurer → organisation: What an underwriter needs before pricing
The underwriter should first specify the proposition it is considering: for example, whether a payment agent may replace a beneficiary without effective independent enforcement, what limits apply and whether exceptions can be detected and reconstructed. An information request should identify the relevant products, exposure period, transaction populations and policy questions. A broker can help preserve the scope and limitations of representations made in placement materials.
Organisation → insurer: How the institution can substantiate controls
Management should provide an accurate account of control design, deployment configuration, observed operation, exception handling and known evidence limitations. Appropriate records may include the authority policy and versions, original instructions, resolved payment details, approval events, decision logs, rejection paths, reconciliation and independent examination reports. Sharing must respect confidentiality, cybersecurity, privacy, lawful retention and access controls. Insurers decide whether and how such evidence influences underwriting; this article makes no claim about premiums, available cover or claims payment.
| Executive or underwriting question | Evidence to examine | What it can show | What remains uncertain |
|---|---|---|---|
| What authority existed? | Mandate, consent/approval event, signatory roles, version and expiry | Recorded limits applicable at the relevant time | Customer understanding and legal validity |
| Did the agent change material terms? | Original instruction, resolved recipient/amount, data provenance and change history | Differences between intended, proposed and transformed actions | Unlogged transformations and compromised records |
| Did an independent control enforce the boundary? | Policy rule, decision trace, blocked attempts, reapproval records and negative tests | Whether examined deviations were detected and handled under criteria | Unexamined paths and future failures |
| What was executed? | Payment instruction, rail acknowledgments, transaction IDs and reconciliation | Whether executed fields correspond to recorded authority decisions | Downstream disputes or incomplete settlement data |
| What evidence can an insurer assess? | Control representations, independent examination scope, tested exceptions and remediation status | Basis, observation window and limits of the representations | Whether the insurer uses the evidence; pricing, insurability and coverage |
The table proposes examinable evidence types. It does not report operating effectiveness for an actual system. “What remains uncertain” concerns the evidential limits of this analysis, not legal advice on liability or insurance coverage.
Independent examination must be bounded to a claim
A meaningful examination could ask: For the defined population of AI-initiated payments in Product P during Period T, were beneficiary changes prevented or linked to an approval permitted under the operative authority policy? This is an example of a testable claim, not a completed ODA3 Institute assessment.
An examiner would need the population and completeness basis, applicable policy and software versions, sampling rationale, test criteria, event integrity, exceptions and access restrictions. Relevant population checks include successful and rejected attempts, changed beneficiaries, retries, overrides, reversals, missing events and reconciliation discrepancies. Internal audit, existing payment-control reviews or vendor assurance may be sufficient for some decisions; a separately commissioned examiner is justified only where the intended reliance question and independence requirements warrant it. It may be possible to conclude that a specified sampled control was evidenced within an observation window. That does not demonstrate universal future reliability, the customer’s subjective understanding, legal authorisation in every case or insurance coverage.
Technical malfunction, resulting financial loss, legal liability and policy response are distinct. An agent can behave outside a mandate without a realised loss. A realised loss does not itself establish who is legally liable. An established liability does not guarantee a particular insurance policy will respond.
Board and executive decisions
| Action | Owner | Decision or evidence required; review trigger |
|---|---|---|
| Establish the authority boundary | Product executive and Chief Risk Officer | Approve permitted payees, amounts, account scopes, standing mandates, amendment rules and escalation; revisit on new payment capabilities or markets |
| Test enforcement at the execution boundary | Chief Information Security Officer and payments engineering | Verify that changed recipients, excessive values and delegated tool calls are blocked or correctly reapproved; revisit on architecture changes or negative-test failures |
| Preserve a complete, protected evidence chain | Operations, privacy and compliance leads | Link approval, policy decision, transaction and reconciliation under proportionate retention and access rules; revisit when records or population counts are incomplete |
| Determine the examination needed before external reliance claims | Risk Committee or designated assurance owner | Decide whether existing internal audit/control evidence suffices or an independent examination is necessary for a specific insurer/regulator reliance question; define criteria, population, period and exceptions |
| Keep underwriting representations and coverage analysis separate | Head of insurance and General Counsel | Record what was asserted, examined and disclosed against actual policy terms; revisit at renewal or material exposure change |
The practical decision is to require an explicit demonstration of agent authority for consequential transactions before relying on broad statements that payments are “approved” or “secure.” How the institution implements that requirement must reflect its legal obligations, product design and existing payment mandates.
Notably Absent
The public sources reviewed do not establish a documented deployment of the synthetic workflow, a real failure of an agentic payment-authority control, or the efficacy of any proposed implementation. No specific bank’s execution records or independently examined deployment outcomes underpin the operational conclusions in this article. No P3P or Gullak operational records were examined; the reference is to published descriptions, not validated performance.
Nor do those sources establish a measured rate of agent-caused unauthorised payments, any insurer’s reliance on the proposed records, any resulting premium differential, or any specific policy response. A jurisdiction-wide legal conclusion about consent or liability cannot be drawn from the governance report and authentication directions alone.
Finally, the sources do not establish that cryptographic signatures, immutable logs or particular agent architectures are universally mandated for all AI-originated financial transactions. The article’s evidence design is ODA3 Institute analysis, not a regulatory specification or an empirical result. Absence from the sources examined does not prove these events or requirements do not exist elsewhere.
Conclusion
Before relying on an AI payment-control claim, a financial institution should establish who authenticated, what authority was in force, what its systems enforced and what was executed. This provides a defined basis for management to examine the controls and evidence an insurer could consider when assessing the exposure. Whether an insurer relies on it, or whether it establishes legal consent or changes policy terms, remains untested and depends on the actual records, applicable law and contract.
References
[1] Reserve Bank of India. “Report of the Committee on Framework for Responsible and Ethical Enablement of Artificial Intelligence (FREE-AI) in the Financial Sector.” Reserve Bank of India, 13 August 2025. https://rbi.org.in/scripts/PublicationReportDetails.aspx?ID=1306 (accessed 26 October 2026). Committee report; not itself a binding transaction-authorisation mandate.
[2] Reserve Bank of India. “Authentication mechanisms for digital payment transactions Directions, 2025.” Reserve Bank of India, RBI/2025-26/79, 25 September 2025, paragraphs 3 and 5. https://www.rbi.org.in/Scripts/NotificationUser.aspx?Id=12898 (direct official text inspected 26 October 2026).
[3] Reserve Bank of India. “Master Directions” index, Reserve Bank of India, entry for “Reserve Bank of India (Commercial Banks – Digital Payment Security Controls) Directions, 2026”, issued 31 July 2026, updated as on 1 October 2026. https://rbi.org.in/scripts/BS_ViewMasDirections.aspx (index checked 26 October 2026). The linked consolidated clause-level text was not accessible in this review.
[4] Pine Labs. “The AI Agent Can Now Pay. Pine Labs Launches P3P — India’s First Agentic Payment Protocol Built on UPI.” Pine Labs, 11 June 2026. https://www.pinelabs.com/media-analyst/the-ai-agent-can-now-pay-pine-labs-launches-p3p-indias-first-agentic-payment-protocol-built-on-upi (accessed 26 October 2026). Company statement; deployment and performance claims have not been independently validated.
[5] Pine Labs. “Pine Labs Payment Protocol — Quickstart.” Pine Labs developer documentation, publication date not stated. https://www.pinelabs.com/docs/online-payments/ai/p3p/quickstart (accessed 26 October 2026). Describes supported payment methods; not independent certification.
Methodology note
Evidence-design analysis with synthetic scenario; no observed production finding; four-record transaction authority chain
Notably Absent
No examined bank deployment, incident prevalence, independent P3P/Gullak testing, insurer reliance, premium or coverage conclusion, universal AI-specific mandate