ODA3-2026-05-INS-021
MCP Security Insights: Risk and Mitigation Strategies
In the twelve months since the Model Context Protocol became the de facto interface layer for enterprise AI automation, the security posture of most.
Read publication →AI SECURITY RESEARCH · PRACTITIONER GUIDANCE
Published research, incident analysis, regulatory context and practitioner guidance. Each article should be read with its stated sources, scope and limits.
Open to read · Publication counts below reflect the published records currently available on this site.
Check the publication ID and date, the source basis, the claim being made and its limits. A published article does not by itself establish an assessment, certification or finding about a particular system. Corrections should remain visible and point to the current authoritative version.
PUBLICATIONS
The catalog includes the published WordPress records available on this site. Search matches titles, article text, publication IDs, tags and recorded evidence-basis fields. Category and year narrow the results; sort changes their order. A match is a retrieval result, not an endorsement or evidence-tier judgment.
ODA3-2026-05-INS-021
In the twelve months since the Model Context Protocol became the de facto interface layer for enterprise AI automation, the security posture of most.
Read publication →ODA3-2026-05-INS-022
The National Institute of Standards and Technology just announced an AI-speci c Cybersecurity Framework pro le — plus predictive and agentic overlays..
Read publication →ODA3-2026-05-INS-023
74 Days to EU AI Act Enforcement — Are Your Controls Ready? On 2 the amended EU AI Act timetable — 74 days from today — the EU AI Act’s prohibitions and…
Read publication →ODA3-2026-05-INS-024
OWASP’s Q1 2026 exploit round-up and the emerging ASI Top 10 prove that real-world attack patterns now outnumber hypothetical risks.
Read publication →ODA3-2026-05-INS-025
Nine Standards. Zero Interoperability. One August Deadline. When your organization faces an AI incident in the next 90 days — a model hallucination that.
Read publication →ODA3-2026-05-INS-026
OpenAI’s “Trusted Access” framework + the EU AI Act Omnibus just rewrote the rules for frontier model governance. Target Audience: CISOs, AI governance.
Read publication →ODA3-2026-05-INS-027
The incident that changed how security teams think about agentic AI did not involve an adversary. There was no attacker, no ex ltration payload, no.
Read publication →ODA3-2026-05-INS-028
NIST’s shift toward threat-based CVE enrichment re ects a broader industry transition from static scoring to dynamic risk contextualization. Organizations.
Read publication →ODA3-2026-05-INS-029
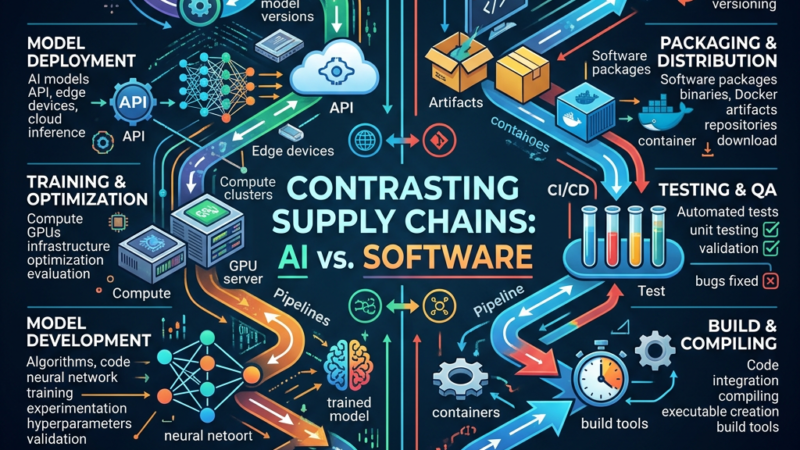
Traditional Software Supply Chain Security Fails for AI In Q1 2026, AI dependency attacks surged 340% year-overyear. Your CVE scanners, static composition.
Read publication →ODA3-2026-05-INS-030
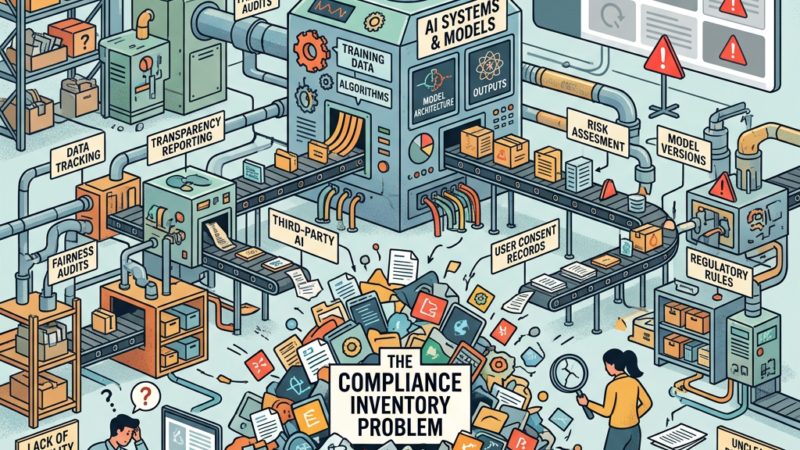
Ask a CISO how many AI systems their organization operates and the most common answer is not a number — it is a pause. Then an estimate. Then a quali er..
Read publication →ODA3-2026-05-INS-031
Emerging discussions at the 2026 AI Security Summit highlight accelerating alignment between AI threat landscapes and international certi cation.
Read publication →ODA3-2026-05-INS-033
If your board asked tomorrow—”What percentage of our AI systems have we inventoried, and what is our con dence score?”—could management answer with 90%.
Read publication →